Demystifying Gate-Level Localization of RTL Trojans
By Navid Nader Tehrani 1, Azadeh Davoodi 1, Rasit Onur Topaloglu 2
1 University of Wisconsin-Madison, USA
2 Marist University, Poughkeepsie, NY, USA
Abstract
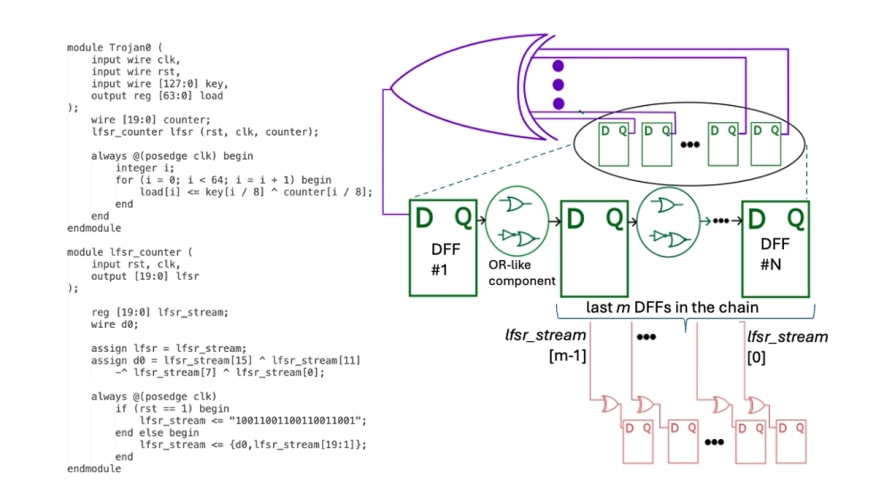
Hardware Trojans are malicious modifications that compromise functionality or leak sensitive data. They pose a severe threat, particularly when inserted at the Register Transfer Level (RTL). After synthesis, these Trojans are often concealed by optimizations in gate-level netlists. Recent efforts, including the ICCAD 2025 contest, emphasize golden-chip-free detection using machine learning (ML) on labeled netlists. In this work, we show that RTL Trojans exhibit stable structural and signal-flow patterns post-synthesis, enabling effective detection through targeted heuristics rather than generic ML feature learning. We propose LoRD, a lightweight heuristic-based approach that exploits these distinctive subgraph signatures, achieving near-perfect detection and localization on the contest testcases. Compared to a transformer-based ML baseline and top five teams, LoRD achieves on-average a score of 2.957 (out of 3) for Trojan- implanted designs without the data and tuning overhead.
To read the full article, click here
Related Semiconductor IP
Related Articles
- A Survey on the Design, Detection, and Prevention of Pre-Silicon Hardware Trojans
- TROJAN-GUARD: Hardware Trojans Detection Using GNN in RTL Designs
- Intellectual-property vendors look beyond RTL
- RTL Prototyping Brings Hardware Speeds to Functional Verification
Latest Articles
- VSpector: Specification-Driven Bug Detection for RISC-V CPUs
- Demystifying Gate-Level Localization of RTL Trojans
- Can Agents Design Better Chips with a Higher Level Abstraction?
- FlexSpIM: An Event-Based Digital Compute-In-Memory Accelerator with Flexible Operand Resolution and Layer-Wise Hybrid Stationarity
- MeshKV: A Network-on-Chip KV Cache Fabric for Scalable Transformer Decoding Accelerators