Vendor: PUFsecurity Category: Root Of Trust

Embedded Hardware Security Module for Automotive and Advanced Applications

PUFhsm is an embedded Hardware Security Module solution for automotive chips and general applications.

Overview

PUFhsm is an embedded Hardware Security Module solution for automotive chips and general advanced applications. It is the latest offering from PUFsecurity that integrates CPU, hardware Cryptographic engines, and software modules for all security applications. This best serves chip designers looking to boost security levels in various applications.

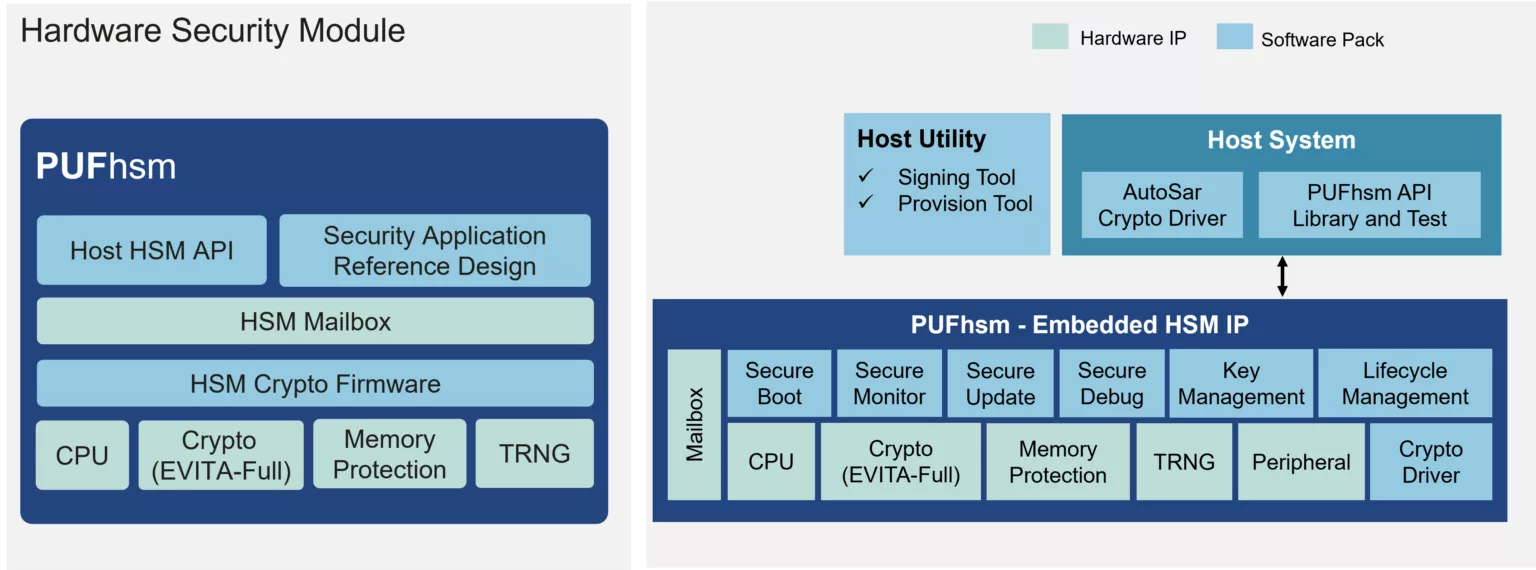
PUFhsm’s key advantage is to support more complete security applications and be more user-friendly. It is positioned as an “Embedded Security Enclave,” which enables the isolation of critical security information from the main system, further enhancing the overall security level. In addition, the PUFhsm architecture features a CPU core in charge of all security instructions within the subsystem. Developers can leave composite security functions to the IP package, including secure boot, secure updates, secure deployment, key management, lifecycle management, secure debugging, and secure monitoring. On top of that, with security operations in PUFhsm, the main CPU is relieved from needing to dispatch security operations. These traits are particularly beneficial for users who are new to introducing security design into SoC, looking to optimize the efficient utilization of the main system’s resources, or plan to fulfill more security applications.

PUFhsm is designed to meet the stringent requirements of EVITA-Full, the highest level of security in the EVITA (E-safety Vehicle Intrusion Protected Applications). EVITA-Full is a benchmark for safeguarding critical automotive applications against sophisticated cybersecurity threats. Its requirements include preventing hardware tampering, ensuring the confidentiality of sensitive data, platform integrity, and authenticity of in-vehicle software and communications. This leads to the requirement of hardware-based cryptographic engines, secure key management, and comprehensive tamper resistance.

Designers also have the option to further improve the security level and anti-tampering by adopting PUFrt with PUFhsm, while also saving development resources. PUFrt, certified by Riscure’s strict anti-tampering test, provides unique ID / keys(PUF), secure storage(OTP), TRNG, and a full set of anti-tampering designs. The hard IP, such as OTP/PUF, has been verified at 150nm-4nm, which enables clients to reduce the integration effort and enter the mass production process faster. The perfect combination of PUFhsm and PUFrt will once again set a new benchmark for security technology. This total solution meets all the chip security needs from underlying physical components to upper-layer security applications.

We will continue to develop more solutions for the PUFhsm family to apply different market requests such as the light version, Function Safety version, and CPU upgraded version. PUFsecurity is committed to meeting more customers’ needs for security technology and helping customers’ products become more secure and competitive.
Key features

  • Pre-integrated CPU
  • Full suite of hardware-accelerate cryptographic engine (Meet EVITA-Full requirements)
  • Complete SDK with APIs for HSM operations to support chip security applications.
  • MailBox Interface to facilitate communication between the main system and HSM.
  • Reference Codes for each security function, simplifying integration.
  • Hardware Abstraction Layers (HALs) for seamless hardware communication.
  • PC Utility with GUI for generating ROM code and firmware as per security needs.
  • Comprehensive Anti-Tamper Designs

Block Diagram

Applications

  • EVITA-Full Compliance: Develops security architecture compliant with EVITA-Full for automotive systems
  • Secure Boot: Ensures authenticity and integrity of all code before execution
  • Secure Update: Verifies only authenticated, authorized firmware is applied
  • Secure Provisioning: Manages secure provisioning of critical components
  • Key Management: Handles key generation, import/export, and use in cryptographic operations.
  • Lifecycle Management: Controls secure access across all lifecycle states, from manufacturing to decommissioning.
  • Secure Debug: Limits debug access to authorized personnel during development
  • Secure Monitor: Provides a trusted environment, isolating sensitive memory and operations

Specifications

Identity

Part Number
PUFhsm
Vendor
PUFsecurity
Type
Silicon IP

Files

Note: some files may require an NDA depending on provider policy.

Provider

HQ: Taiwan

Learn more about Root Of Trust IP core

Embracing a More Secure Era with TLS 1.3

TLS 1.3 offers attractive speed and security improvement benefits that are hard to ignore. The handshake phase was sped up by removing one or more roundtrips (back and forth messaging between client and server) in TLS 1.3 – with “or more” meaning that for certain cases, roundtrips can be entirely eliminated (0-RTT).

The Challenge of Automotive Hardware Security Deployment

A complete reinvention of the automotive industry is currently underway. Autonomous driving, connected vehicles, and the electrification of the powertrain all represent a once-in-a-generation shift in the manufacturing process.

Why Hardware Root of Trust Needs Anti-Tampering Design

The hardware root of trust (HRoT) provides the trust base (root key), hardware identifier (UID), hardware unique key (HUK), and entropy required for the secure operation of the entire chip and therefore is often the focus of hacker attacks. If the design can’t effectively resist attacks, hackers can easily obtain the secrets of the entire chip. Attackers can use the secrets to crack identity authentication and data encryption and steal product design know-how, causing application security problems.

TPM 2.0-Ready: Top Security with PUFcc

The rising security threats endangering our connected world, from the chip to the cloud, are among the biggest challenges facing us today. Microsoft recently addressed some of these concerns by mandating the inclusion of TPM 2.0 (Trusted Platform Module) in all devices running its latest Windows 11 operating system. I

Solving Chip Security's Weakest Link

With the invention of Physical Unclonable Functions (PUF), we can now create a unique, inborn, unclonable key at the hardware level. The natural follow-up question to this is, “but how do we protect this key?” It is like storing your key to secrets in a drawer, a surefire way to break the secure boundary and create vulnerabilities.

Frequently asked questions about Root of Trust IP cores

What is Embedded Hardware Security Module for Automotive and Advanced Applications?

Embedded Hardware Security Module for Automotive and Advanced Applications is a Root Of Trust IP core from PUFsecurity listed on Semi IP Hub.

How should engineers evaluate this Root Of Trust?

Engineers should review the overview, key features, supported foundries and nodes, maturity, deliverables, and provider information before shortlisting this Root Of Trust IP.

Can this semiconductor IP be compared with similar products?

Yes. Buyers can compare this product with similar semiconductor IP cores or IP families based on category, provider, process options, and structured technical specifications.

×
Semiconductor IP